Open-Source vs. Proprietary Software choices shape budgets, timelines, and control for teams in 2026. Readers deciding between models need a clear view of licensing, cost drivers, and operational trade-offs before they commit. This guide defines both models, compares ownership and total cost of ownership, and walks through security, support, and flexibility trade-offs so decision makers can match software strategy to business constraints.
Key Trade-Offs Between Open-Source and Proprietary Software
- Open-source software offers transparency and allows immediate bug fixes, enabling faster operational responses compared to proprietary software’s vendor-dependent patch cycles.
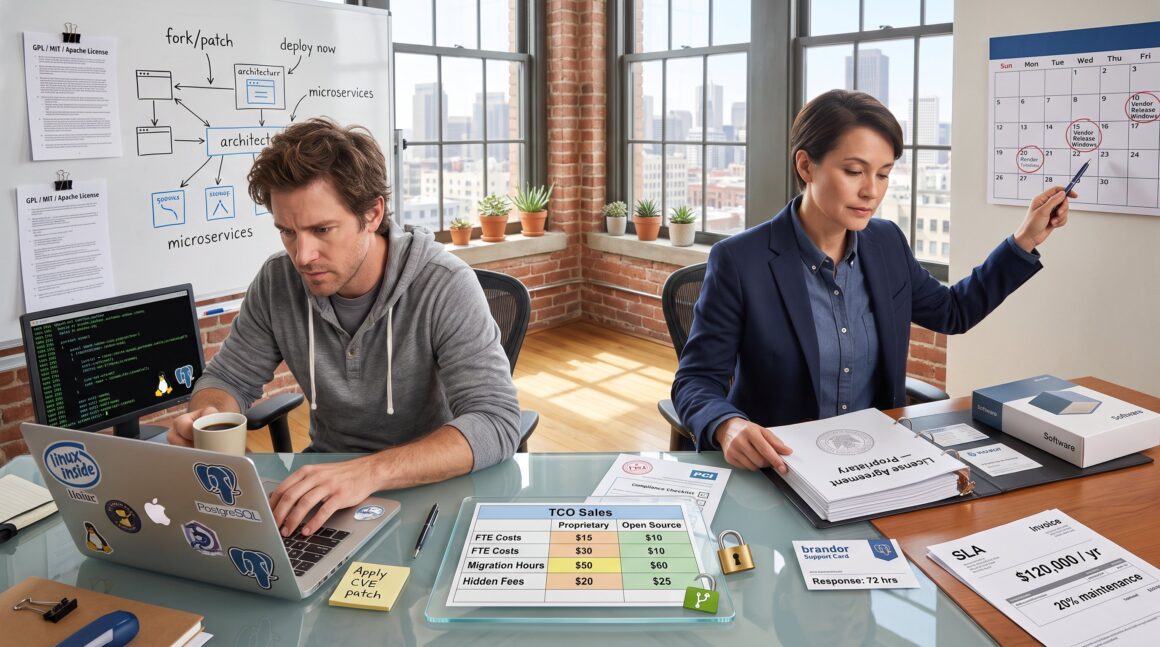
- Total cost of ownership includes not only license fees but also engineering effort, customization, support, and compliance costs, which vary for open-source and proprietary models.
- Open-source provides deep customization and control but requires careful governance to avoid security risks from delayed patching.
- Proprietary software offers predictable vendor-managed security, support contracts, and indemnities, beneficial for regulated organizations needing stable SLAs.
- Vendor lock-in in proprietary solutions can mean costly migrations, while open-source reduces this risk but may increase maintenance burdens from custom forks.
- Planning and budgeting for hidden costs like training, support contracts, and emergency fixes are essential to accurately compare open-source and proprietary software investments.
Defining Open-Source And Proprietary Models
Fact: Open-source software publishes source code: proprietary software keeps code closed and controlled. Open-source projects, examples include the Linux kernel and PostgreSQL, ship with licenses like GPL, MIT, or Apache that let users inspect, modify, and redistribute code under set terms. Proprietary vendors such as major ERP or desktop app providers distribute compiled binaries and sell usage rights under restrictive licenses.
Context and detail: In practice, a team that needs to fix a bug today can patch an open-source component immediately if they have developers on staff. By contrast, a team using proprietary software often files a ticket and waits for a vendor patch tied to a release cadence. That difference affects lead time: an internal patch takes hours or days: vendor-driven fixes can take weeks or quarters.
Concrete example: A fintech startup discovered a data-format mismatch in an open-source library and pushed a fix in two days: the same issue in a closed-source payment gateway required a support SLA escalation and a 10‑day wait. This illustrates how access to code translates to real operational speed and control.
Cost, Ownership, And Total Cost Of Ownership
Fact: License fees are not the whole cost, TCO depends on staff, customization, and scale. Open-source often removes upfront license fees but shifts costs into engineering time: deployment, integration, and ongoing maintenance. Proprietary software charges license or subscription fees and typically bundles vendor responsibility for maintenance.
Details and numbers: For a mid-size company, an open-source stack might avoid $50k–$120k in annual licenses but require 1.0–2.5 full-time equivalents (FTEs) for operations, costing roughly $100k–$250k per year. A proprietary vendor may charge $120k per year yet include SLA-backed support and managed upgrades. Neither option is universally cheaper: the math depends on the organization’s wage rates, required uptime, and customization scope.
Hidden costs to watch: migration expenses, training, and compliance audits can add tens of thousands of dollars. One real case: a retail firm saved $90k in license fees but spent $140k customizing and validating open-source components for PCI compliance in year one. That mistake, underestimating compliance work, was costly but instructive.
Practical decision rule: estimate internal FTE needs, add third-party support if required, and compare that sum to vendor fees and maintenance percentages to compute TCO over 3–5 years.
Security, Support, And Flexibility Trade-Offs
Fact: Open-source gives transparency and community scrutiny: proprietary gives vendor-managed security and predictable SLAs. Transparency means anyone can audit open-source code: in several incidents, community review found critical bugs faster than vendors did. Conversely, proprietary vendors provide defined patch windows, indemnities, and support contracts that some regulated firms rely on.
Evidence and nuance: Independent audits show that both models can be secure when governed properly. A bank might prefer a vendor with an ISO certification and a legal indemnity, while a cloud platform team may prefer open-source components they can fork and harden. Flexibility differences are stark: open-source allows forks and deep customization: proprietary platforms often limit change to configuration or paid extensions.
Link and resource: For teams comparing models across product types and business needs, a high-level reference on broader technology strategy helps frame practical choices: a concise overview is available in the site primer on technology and tools such as the technology overview.
Warning: transparency helps but does not equal safety. If an organization lacks governance, public code can become an attack vector. The honest lesson: visibility without process created a breach for one small healthcare provider that failed to apply a community patch for 45 days.
Patch Management, Vendor Lock-In, And Customization
Fact: Patch cadence, lock‑in risk, and customization effort differ sharply between models. Open-source lets teams apply or backport patches on their schedule: proprietary products usually follow vendor patch cycles and require acceptance testing per release.
Patch management example: An operations team applied a security backport to an open-source database the same day a CVE was published: it took a proprietary vendor three release cycles to include the same fix. That lag created measurable exposure.
Vendor lock-in specifics: Proprietary lock-in manifests as closed data formats, expensive migration tools, and long contracts. One company measured migration effort from a closed CRM to an alternative at 1,200 engineering hours and $180k tooling plus consulting, real costs that drove their multi-year commitment. Open-source reduces some migration costs because formats often stay open, but heavy customization can create its own exit barriers.
Customization trade-offs: Open-source customization is deep but increases maintenance burden: every fork must be rebased against upstream releases. Proprietary customization is usually limited to configuration or vendor-provided extensions, which preserve easier upgrades but cap flexibility. Teams should inventory custom changes and model upgrade costs before choosing.
Related guidance: For hardware and gadget-style comparisons, deciding which components to prioritize, gadget comparison tips.
Licensing, Access, And Development Differences
Fact: Licenses determine rights to modify, redistribute, and fork. Open-source licenses vary: GPL demands share-alike for derivatives: MIT/Apache are permissive and allow proprietary derivative works. Proprietary licenses normally forbid redistribution and limit installations and users.
Development model contrast: Open-source development is often distributed and community-driven. Contributors across firms and hobbyists submit patches and iterate rapidly. Proprietary development is centralized: a single vendor controls roadmaps, feature prioritization, and release schedules. This control delivers predictable product direction but can ignore niche customer needs.
Concrete developer scenario: A payments team needed a new auth connector: with an open-source stack they could build and upstream it, benefitting the community and reducing future maintenance. With a proprietary product, they requested a feature and were given a multi-quarter roadmap slot, too slow for the launch.
Advice: map required license obligations (attribution, redistribution, copyleft triggers) before embedding an open-source component into commercial products to avoid legal surprises.
Hidden Costs, Support Contracts, And Licensing Fees
Fact: Hidden support and licensing costs appear in both models, but they come from different places. Open-source hidden costs often equal implementation, staff training, and optional paid support. Proprietary hidden costs show up as maintenance fees (commonly 18–25% of license cost), version upgrades, and paid integrations.
Specific numbers: Many vendors set annual maintenance at roughly 20% of the initial license. In one procurement review, that recurring fee doubled three-year spend projections compared with the first-year license. For open-source, purchasing commercial support for mission‑critical components commonly runs $20k–$150k per year depending on scale.
Real lesson: A nonprofit assumed open-source meant low cost and skipped budgeting for support: when incidents occurred, emergency contracting cost 2.3x expected annual support and disrupted operations. The takeaway: budget for support early, either as vendor SLAs or retained engineering hours.
Operational tip: include a contingency line in TCO models for emergency fixes and compatibility work, 10–25% of projected maintenance is a practical starting point.