Cybersecurity Basics Every Technology User Should Understand is essential reading for anyone who stores sensitive data on a phone, laptop, or cloud account. In 2026, attackers still rely on social engineering, credential theft, and ransomware to turn a single click into financial loss or identity fraud. This article explains why ordinary users matter in the security chain, the specific threats to watch for, and clear, practical habits they can adopt today to reduce risk.
Key Takeaways
- Every technology user plays a crucial role in cybersecurity by adopting safe habits to protect devices and data.
- Cybersecurity basics include recognizing common threats like phishing, malware, and credential attacks that rely on human error.
- Using unique passwords managed by a password manager significantly reduces risks from credential reuse and credential stuffing attacks.
- Enabling multi-factor authentication (MFA) or passkeys provides a strong layer of security, blocking access even if passwords are compromised.
- Regular automatic updates and tested backups are essential to protect against vulnerabilities and data loss, ensuring fast recovery from attacks.
- Being cautious with links, attachments, public Wi-Fi, and adding layered defenses like device encryption dramatically lowers the chance of successful breaches.
Why Cybersecurity Matters For Every User Today
Fact first: Most breaches start with people, not perfect malware. Social engineering and credential theft now account for a large share of intrusions, and attackers probe everyday devices to reach bigger targets.
Everyday devices store direct paths to money and identity. A phone often holds banking apps, two-factor tokens, and personal health records. A reused password on a laptop can give an attacker access to work email and cloud drives. In 2025 incident reports, adversaries frequently leveraged stolen credentials to move laterally inside organizations and monetize access quickly. That pattern means a single compromised home device can ripple into larger incidents.
Why this matters to the reader: they are a node in other people’s security. Family members, contractors, and small business employees often use the same services. Weak practices, password reuse, delayed updates, or unverified attachments, create predictable windows for attackers.
A practical example: an employee opens a convincing invoice PDF sent to their personal address. The PDF contains a credential harvester that captures a reused login. The attacker then uses that login to request password resets at corporate services, bypassing perimeter defenses. That sequence begins with a simple human lapse.
For readers comparing hardware decisions, practical buying advice can help: combine product evaluation with security habits. For techniques on judging devices beyond specs, see a short piece on comparing gadgets.
Common Threats Every Technology User Should Know
Fact first: phishing, malware, and credential attacks remain the top risks for everyday users. They are simple for attackers to scale and devastating when successful.
Phishing and social engineering. Attackers create emails, texts, or fake login pages that mimic banks, delivery services, or workplace IT. The message often contains a sense of urgency, “confirm payment” or “unlock your account”, and a plausible sender name. When a user types credentials into a spoofed page, attackers capture them instantly. A single successful phishing message can produce credential pairs that fuel credential stuffing attacks across dozens of sites.
Malware and ransomware. Malicious software ranges from information stealers that quietly extract saved passwords to ransomware that encrypts files and demands payment. A user who downloads a cracked app or opens a malicious attachment can trigger system-wide encryption within hours. Ransomware groups publicly list victims and demand payments often in six‑figure ranges for corporate compromises: for individuals, the loss is usually data and time.
Credential attacks. Password reuse and predictable passwords let attackers automate access with leaked credential lists. Credential stuffing tools test reused credentials across hundreds of sites in minutes. Simple defenses, unique passwords and a password manager, stop most credential attacks.
Data exfiltration. Once inside, attackers copy personal or business data to sell or extort. That is why backups matter, but backups must be isolated and tested.
Denial-of-service (DoS/DDoS). While typically targeted at services, DDoS incidents can prevent access to cloud backups or email during an ongoing attack, amplifying damage.
For readers who want a short checklist of core habits tied to these threats, a concise guide explains daily practices and reducing attack surface: a good primer appears in this text on minimalist cybersecurity tips.
Practical Security Habits Every User Can Adopt Right Now
Fact first: three habits, unique passwords, multi-factor authentication, and tested backups, prevent most common attacks. They take modest time but deliver outsized protection.
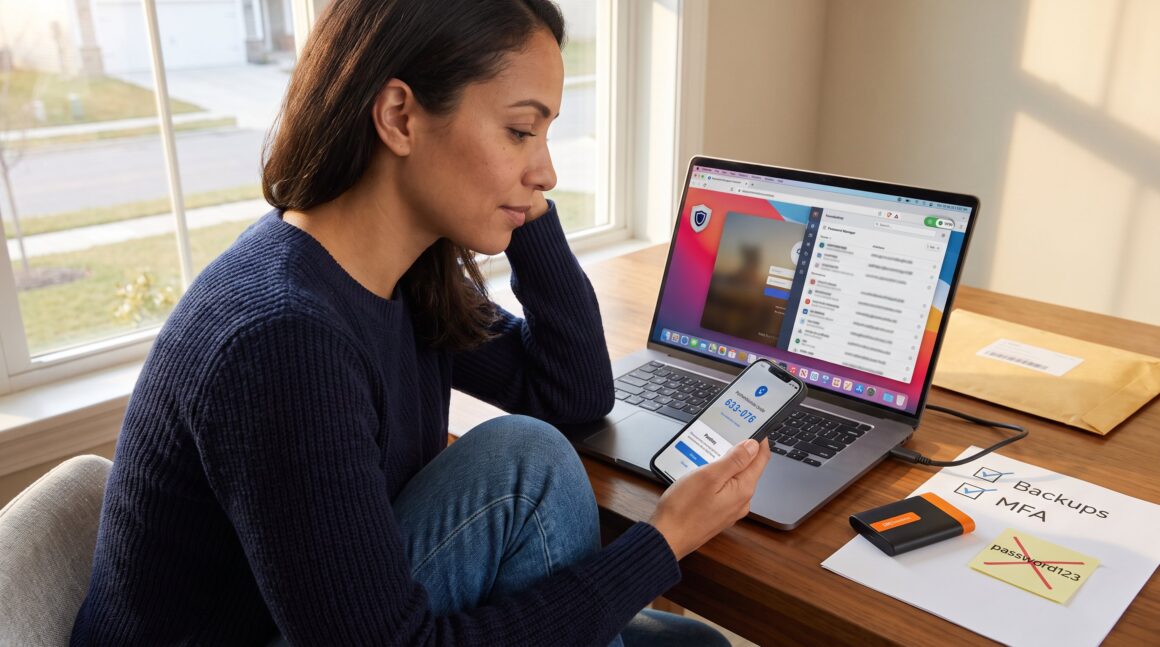
Use a password manager and unique passwords. Password managers generate and store long, random passwords so users avoid reuse. A single manager that covers 50 accounts removes the cognitive burden and closes credential stuffing risk. If a manager holds 2,847 saved logins, losing one weak password no longer compromises hundreds of services.
Enable MFA or passkeys. Multi-factor authentication blocks access even if passwords leak. Where possible, choose hardware-backed passkeys or authentication apps rather than SMS. Attackers still intercept SMS at scale: app-based codes or FIDO2 passkeys reduce that attack vector dramatically.
Turn on automatic updates. Automated OS and app updates patch known vulnerabilities the moment vendors fix them. Delaying updates by a week or month leaves devices exposed to public exploits. For cloud-based backups specifically, understand how cloud providers isolate snapshots: background reading on cloud concepts helps users choose backup strategies and retention, see an explainer on cloud computing.
Back up and test restores. Backups are only useful when they can be restored. Maintain both an online (encrypted cloud) copy and an offline local copy. For critical files, perform a full restore test quarterly. If a restore takes 30 minutes in a test, plan for that downtime in a real incident.
Be cautious with links and attachments. Verify unexpected requests by phone or a second channel. When an email asks for credentials, pause and confirm: a 90‑second call can stop a fraud costing hundreds of dollars.
Protect public Wi‑Fi use. Avoid banking on public Wi‑Fi or use a reputable VPN when necessary. Also lock devices with a PIN or biometric and disable unused radios like Bluetooth when not in use.
Add layered defenses. Use device encryption, enable browser phishing protections, and limit app permissions. For product choices and how to compare security features when buying gadgets, refer to a short guide on how to compare gadgets.
Honest note: people often skip backups because they assume it will never happen to them. That assumption costs time, restoring from zero can take a week and lose recent work. Start with simple steps: set a manager, enable MFA, toggle automatic updates, and run one restore test this month. For a broader site overview and context on technology coverage, see this short site overview.
Conclusion
Users control the simplest, most effective defenses: unique credentials, multi-factor authentication, timely updates, and reliable backups. These habits reduce the chances of a breach and limit damage if one occurs. Start with one habit this week, set up a password manager or enable MFA, and build momentum from there: small, consistent changes compound into meaningful protection.